Proactive
01Threat intelligence
Proactive identification and analysis of emerging cyber threats before they reach your systems. Continuous monitoring, adversary profiling and early-warning systems.
Protecting organisations through strategic security frameworks, threat intelligence and resilient infrastructure, built on deep expertise across enterprise and government environments.
From finding weaknesses before attackers do, to responding when they strike, to advising the board on what it all means.
Proactive identification and analysis of emerging cyber threats before they reach your systems. Continuous monitoring, adversary profiling and early-warning systems.
Authorised simulated attacks on your infrastructure to expose vulnerabilities. Network, web app, social engineering and red team operations.
Rapid containment, investigation and recovery when breaches occur. 24/7 response, forensic analysis, evidence preservation and post-incident hardening.
Building a human firewall: board-level cyber-risk workshops, phishing simulation, OSINT awareness and secure-coding programmes for developers.
End-to-end email hardening: SPF, DKIM and DMARC configuration, anti-phishing controls, business email compromise prevention and staff simulation campaigns.
Continuous scanning and prioritisation across your infrastructure. Automated detection, CVSS scoring, patch tracking and recurring remediation cycles.
Active defence: deception technologies, honeypots, threat hunting and adversarial countermeasures to detect and neutralise attacks in real time.
Executive advisory that translates complex threat landscapes into business risk, security roadmaps, board reporting and long-term resilience planning.
A short conversation to understand your systems and tell you where the real risks are.
Get in touchA free, private check-up for your digital accounts and your organisation. Answer simple questions, get a personal action plan, and step-by-step help if you’ve been hacked.
Can scammers send emails pretending to be your organisation? Enter your domain to check its public anti-spoofing settings (SPF and DMARC).
General guidance based on widely recommended security practice, not a professional audit. App menus can differ slightly between versions. Never share passwords or verification codes with anyone, including this site.
When an organisation’s systems are breached, speed and structure decide the outcome: contain, clean, harden, restore.
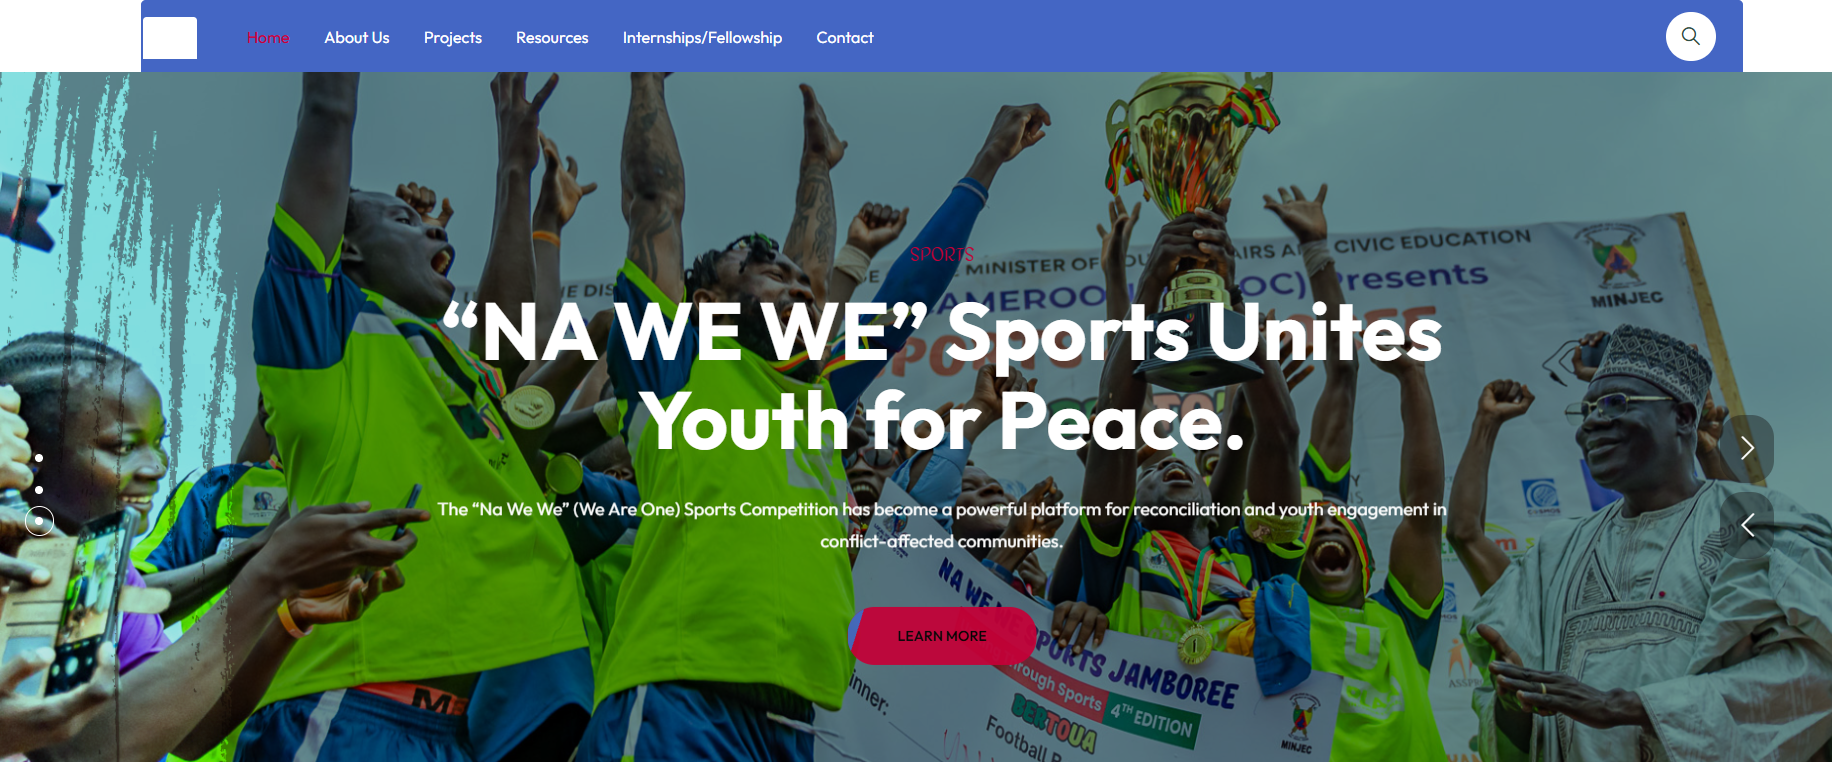
In February 2023, loyocameroon.org was compromised following a successful attack affecting the website environment. I investigated and contained the incident, removed malicious code and files planted within its internal systems and cPanels, secured affected email access, reviewed the compromise path, hardened the hosting environment and rebuilt the backend to restore secure operation.
Local Youth Corner Cameroon (LOYOC) is a leading, award-winning, youth-led non-governmental organization since 2002 empowering young people aged 15 to 35 and promoting peacebuilding across Cameroon and the broader Sahel region.
When public-facing digital assets are compromised, recovery is only the first step: restore access, secure ownership, harden controls, prevent recurrence.
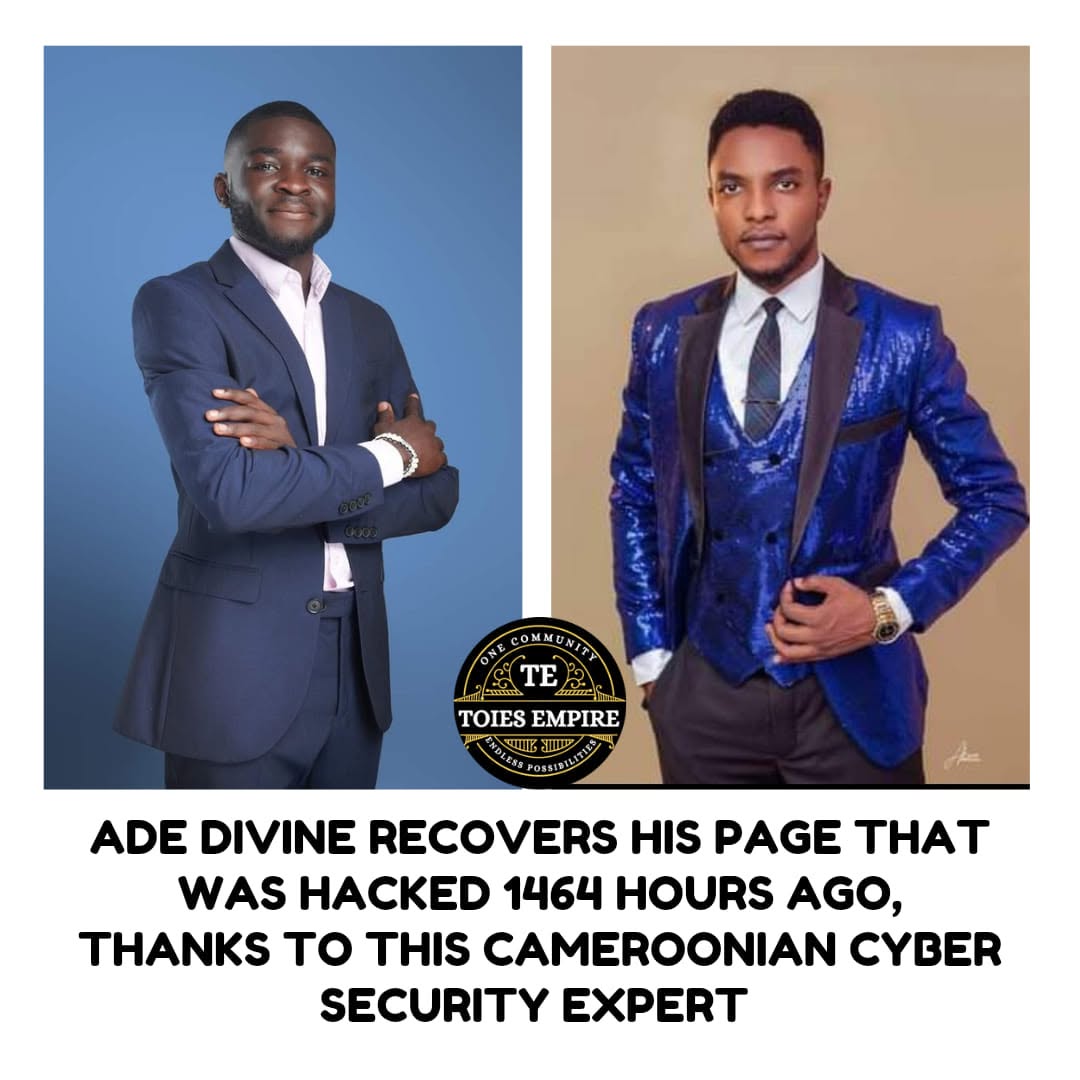
Cameroon’s Most Followed Sports Journalist
I led the recovery of the compromised Facebook page of Ade Divine, one of Cameroon’s most-followed sports journalists, following unauthorised access to the account. The incident involved a high-value digital asset with an audience of more than 203,000 followers, making rapid recovery and restoration of trusted account control critical.
The response involved assessing the compromise, and undertaking more than four weeks of technical recovery. Post-recovery measures included reinforcing authentication, reviewing active access and administrative permissions, and improving the overall security posture of the account.
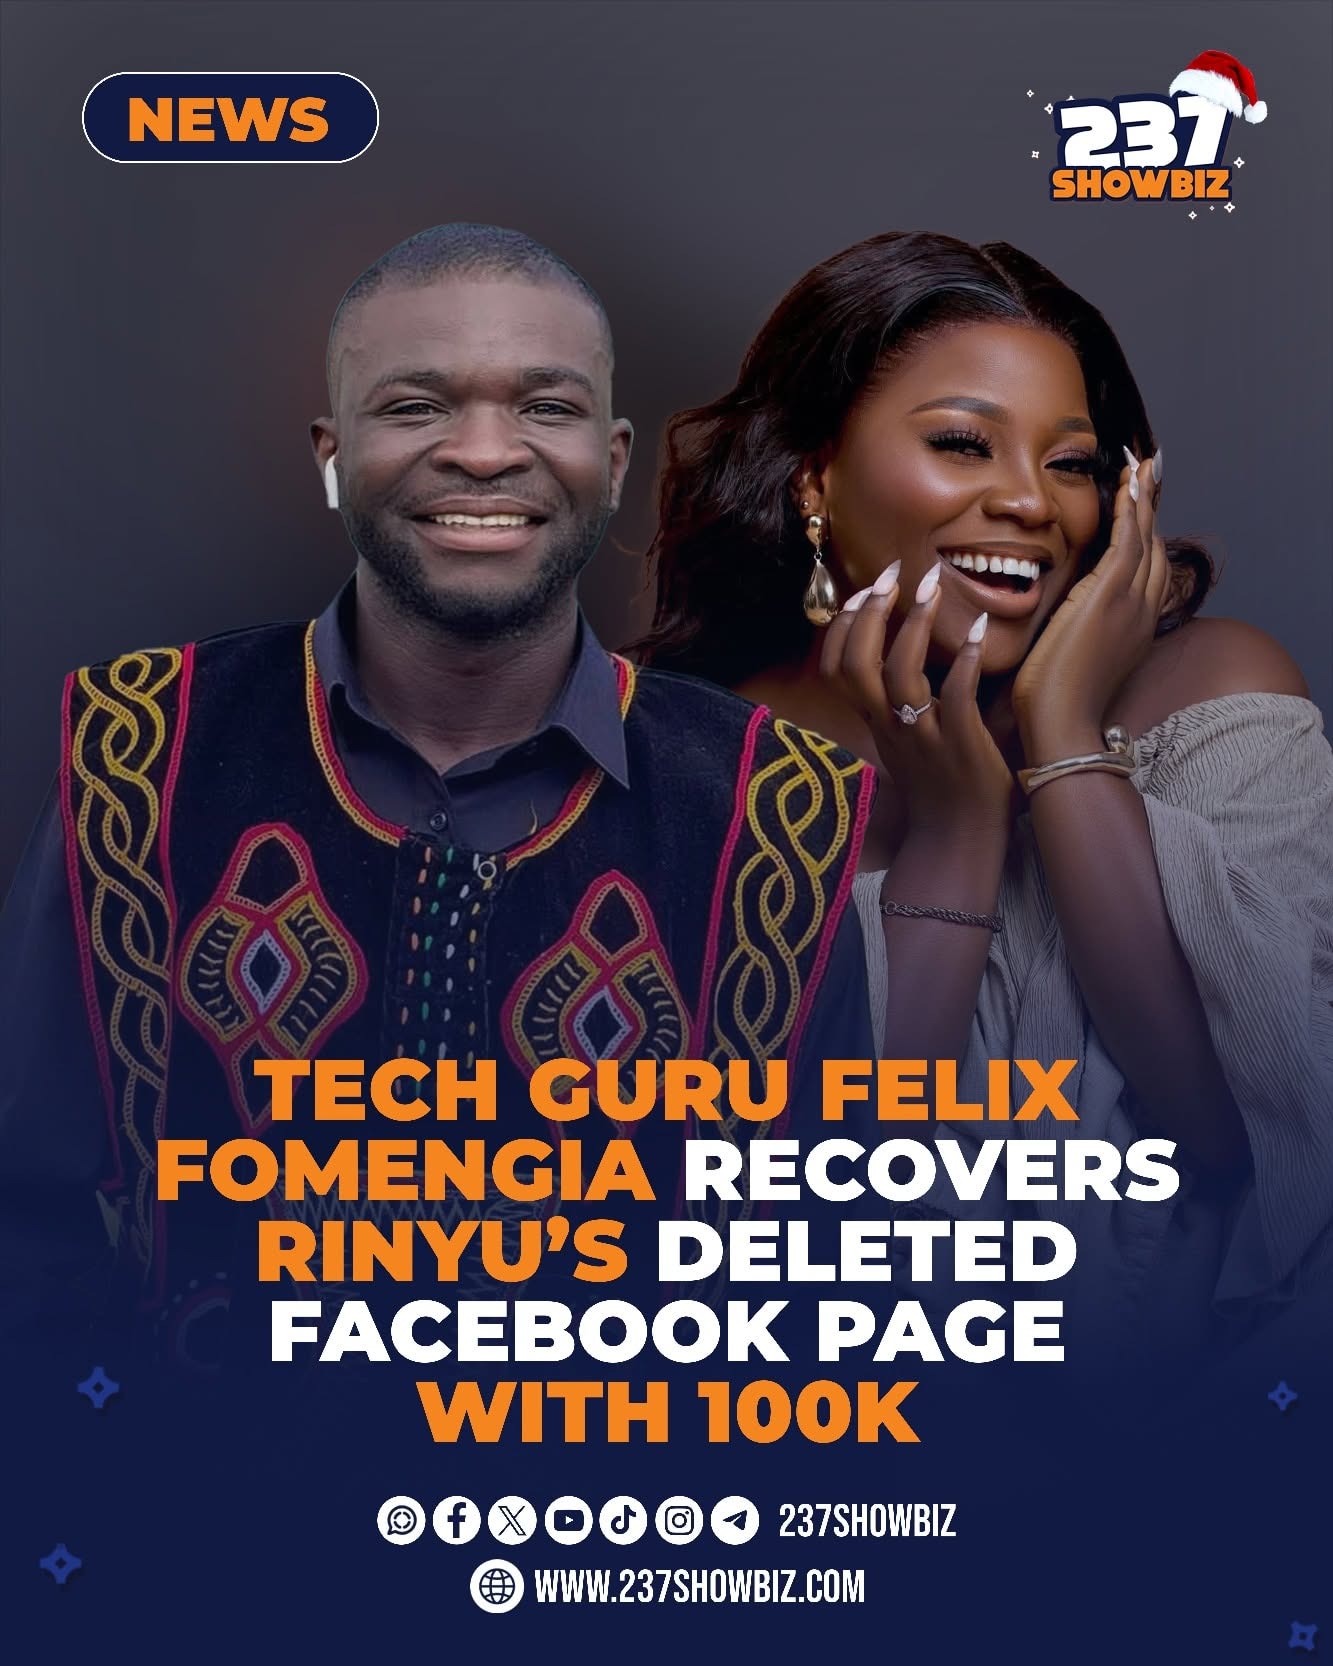
Cameroonian Artist
I led the recovery of the compromised official Facebook page of Cameroonian artist Ngah Rinyu after a cyber incident resulted in the loss of legitimate control over the page and its subsequent deletion by the attackers.
With an audience of more than 110,000 followers, the compromised page represented a significant digital asset. I supported the entire recovery, investigating the compromise and technical response, and strengthening authentication and access controls to reduce the risk of recurrence.
The case demonstrates the importance of treating social-media accounts belonging to public figures as critical digital assets, requiring structured incident response, strong identity controls and post-recovery security measures rather than relying solely on password resets.
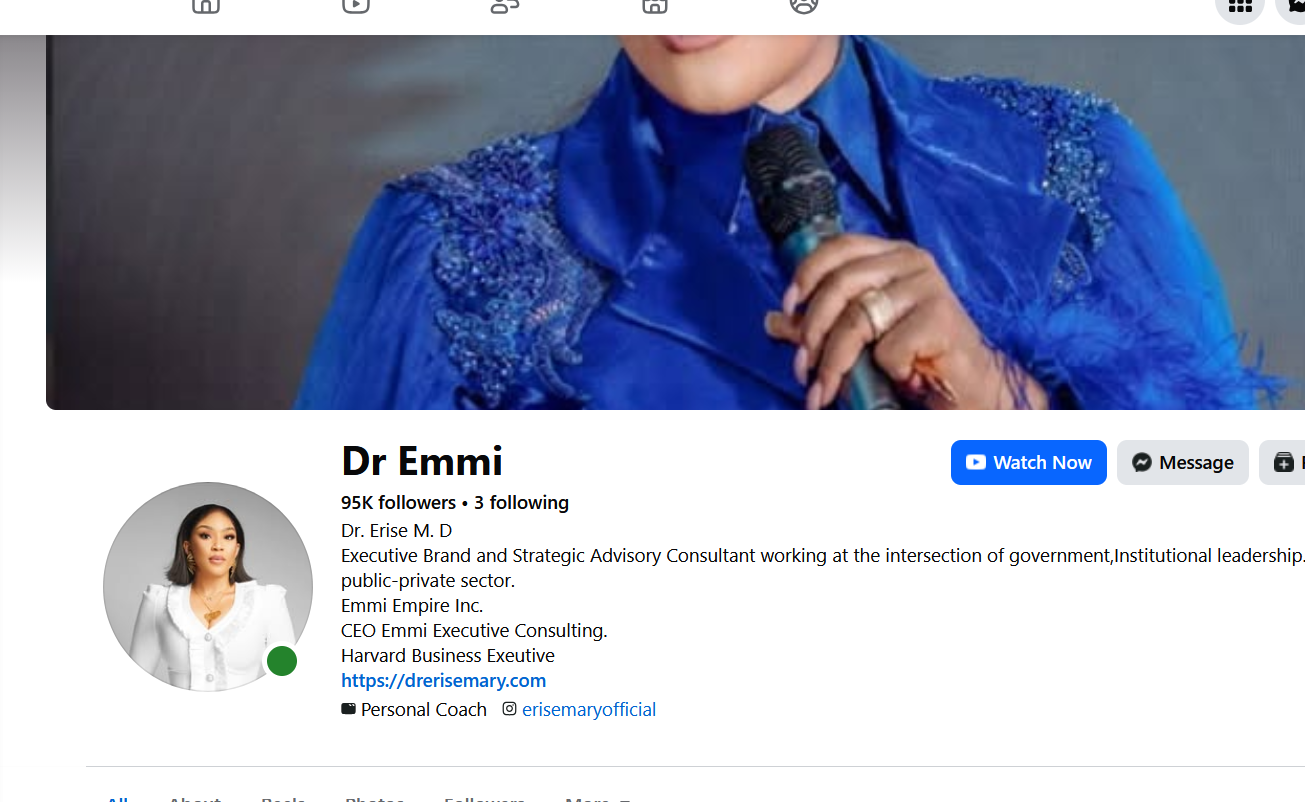
CEO, Emmi Empire
In August 2025, I supported the recovery of the Dr Emmi Facebook page after it was compromised and hacked by a Vietnamese hacker and for over a month misused for unauthorised live streaming. With approximately 95,000 followers, the page represented a significant digital asset.
The recovery required sustained technical intervention to restore legitimate control, completely reclaiming access from the hacker. Emmi Empire publicly acknowledged this cybersecurity expertise as instrumental in the successful recovery.
❯ run security-audit --target client.org
// initialising scan modules...
✓ Network topology mapped [247 nodes]
✓ SSL/TLS certificates validated
⚠ Outdated firmware detected [3 devices]
✓ Firewall rules audited [142 rules]
✗ CVE-2024-3094 — patch required
✓ IAM policies reviewed
⚠ MFA not enforced [12 accounts]
✓ Encryption at rest verified
❯ generate-report --format pdf
✓ Report generated: audit_report.pdf
❯
Five stages, repeated on a cycle, so security keeps pace with your systems as they change.
Asset inventory, attack-surface mapping and stakeholder interviews.
Risk scoring, vulnerability analysis and threat modelling.
Prioritised patching, architecture improvements and new controls.
Zero-trust implementation, policy enforcement and system hardening.
SIEM tuning, continuous monitoring and quarterly reviews.
Focused on two core disciplines: cybersecurity, including the analysis and mitigation of digital risks and threats, and digital forensics, covering the investigation, recovery and examination of digital evidence for legal and investigative purposes.
The MSc Cyber Security and Forensics programme is fully certified by the UK’s National Cyber Security Centre (NCSC), recognising its alignment with national standards for advanced cybersecurity education and its relevance to industry needs.
Hands-on response to real incidents: compromised websites, mailboxes and high-profile social media pages contained, recovered and hardened against repeat attacks.
See the case studiesWhether you need a rapid assessment, ongoing advisory or incident response, let’s talk about securing what matters most to your organisation.
contact@felixfomengia.com